The Challenge
MFA policies can leave hidden gaps across legacy protocols, service accounts, and third-party apps, giving attackers paths to bypass authentication controls and access sensitive workspace data.
Our Solution
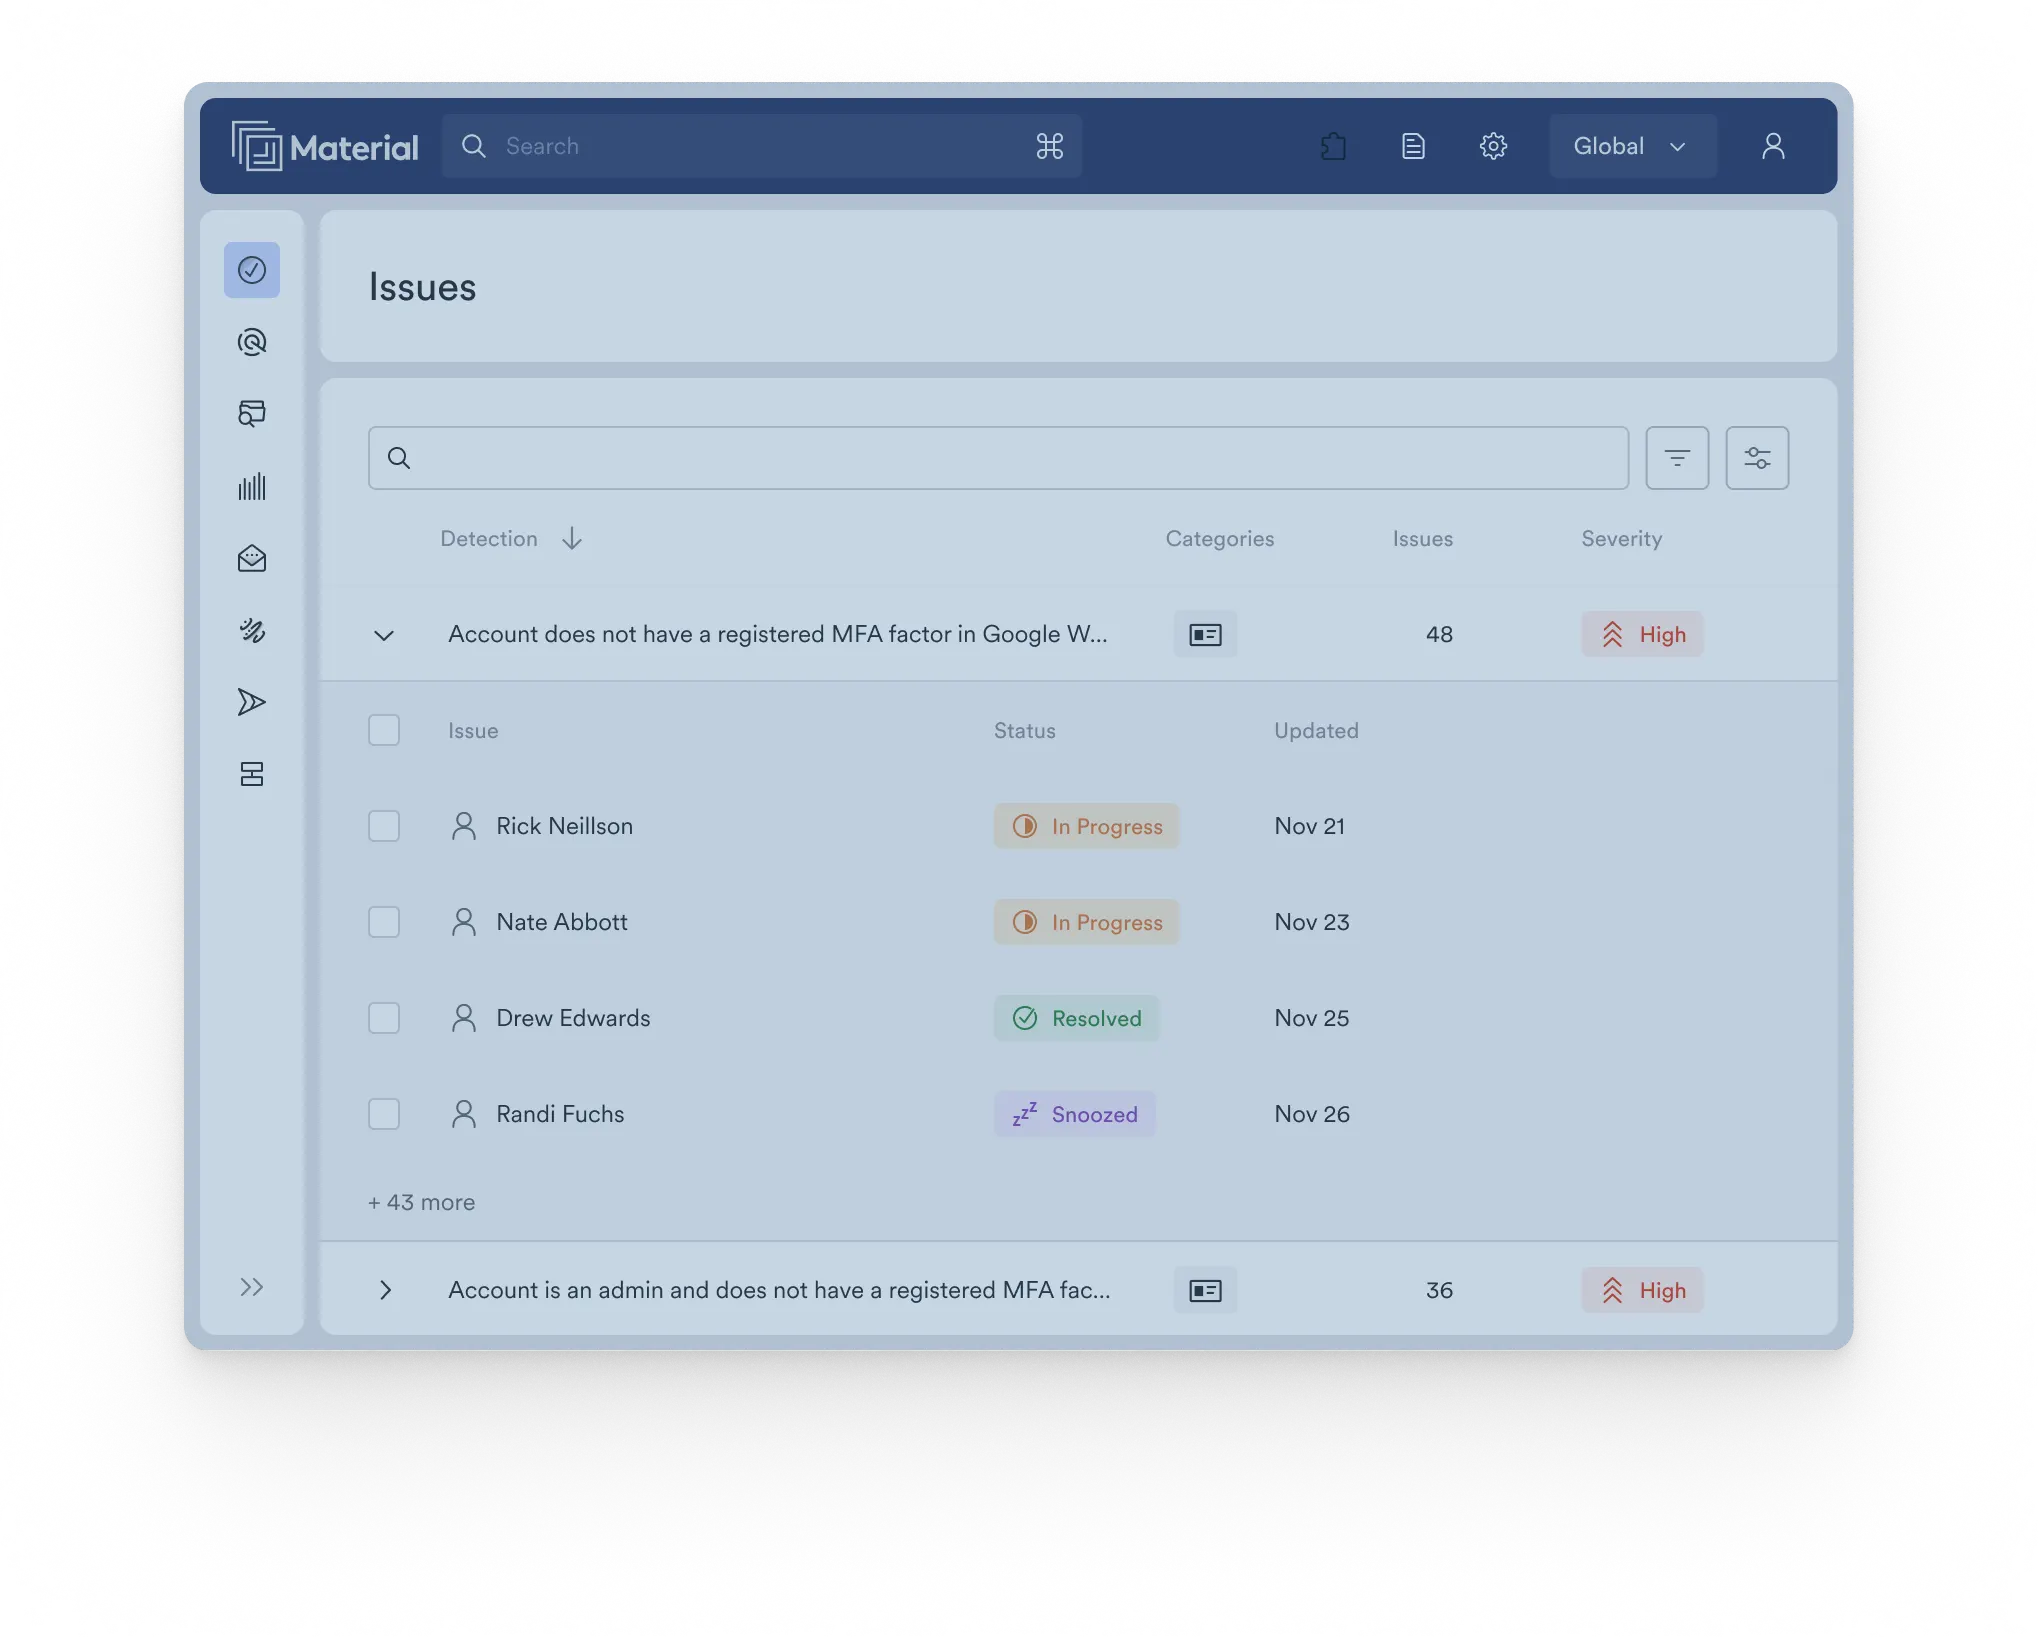
Material continuously verifies your true MFA posture across every account, protocol, and connected app, giving you a single source of truth instead of blind trust in policy configuration.
Hear it from our customers
“We use a lot of SaaS services. Protecting them from inappropriate access is critical. Material gives us peace of mind because it prevents account takeovers even if a particular service is not set up with SSO and MFA.”
 Lisa Hall
Former Head of Information Security, PagerDuty
The Challenge
Your MFA coverage isn't what you think it is
You've invested in an identity provider and rolled out MFA across the organization. Yet, dangerous gaps often persist, invisible to both you and your IdP. These blind spots aren't edge cases; they are common, high-impact vulnerabilities that attackers actively seek out.
- Legacy protocol loopholes Old protocols like IMAP, POP, and SMTP often don't support modern authentication methods. If left enabled on user accounts, they create a backdoor for attackers to access mailboxes with just a password, completely bypassing your MFA policies.
- Service account blind spots Non-human accounts used for scripts and applications are critical for automation but are frequently configured with static, password-only credentials. They are often excluded from MFA policies and become high-value targets for attackers looking for a persistent foothold.
- Third-party app misconfigurations An integrated third-party application granted excessive permissions via OAuth can sometimes provide a path to data that bypasses your primary MFA controls.
- Siloed visibility Your IdP is the front door, but it doesn't have a perfect view of every room in the house. It can't easily see which accounts still have legacy protocols enabled or other risky settings configured directly within Google Workspace or Microsoft 365. There's no single source of truth to confirm your MFA policy is actually being enforced everywhere.
Our Solution
A unified and continuous view of your true security posture
Material acts as the authoritative verification layer for your entire cloud workspace. By integrating directly with Google Workspace and Microsoft 365 via APIs, Material provides a continuous, comprehensive assessment of your security posture, including the true state of your MFA coverage.
- Comprehensive posture analysis Material continuously scans your environment for hundreds of configuration risks. It gives you a single dashboard to see your true posture, immediately flagging accounts and settings that are not properly protected by MFA.
- Identify legacy authentication risks Material automatically detects every user and service account that has legacy protocols enabled. It presents this as a prioritized list, allowing you to systematically disable these backdoors before they can be exploited.
- Surface high-risk accounts The platform identifies both human and non-human accounts with weak authentication settings and enriches this information with context, such as their level of privilege and access to sensitive data, so you can address the biggest risks first.
- Validate identity provider policies Use Material as the source of truth to validate that your IdP policies are working as intended. Material gives you the proof you need to show auditors—and yourself—that your MFA controls are fully deployed and have no hidden gaps.