The Challenge
Cloud workspace settings constantly change across users, teams, and admin consoles, making it difficult to maintain a secure baseline and catch risky deviations before they create exposure.
Our Solution
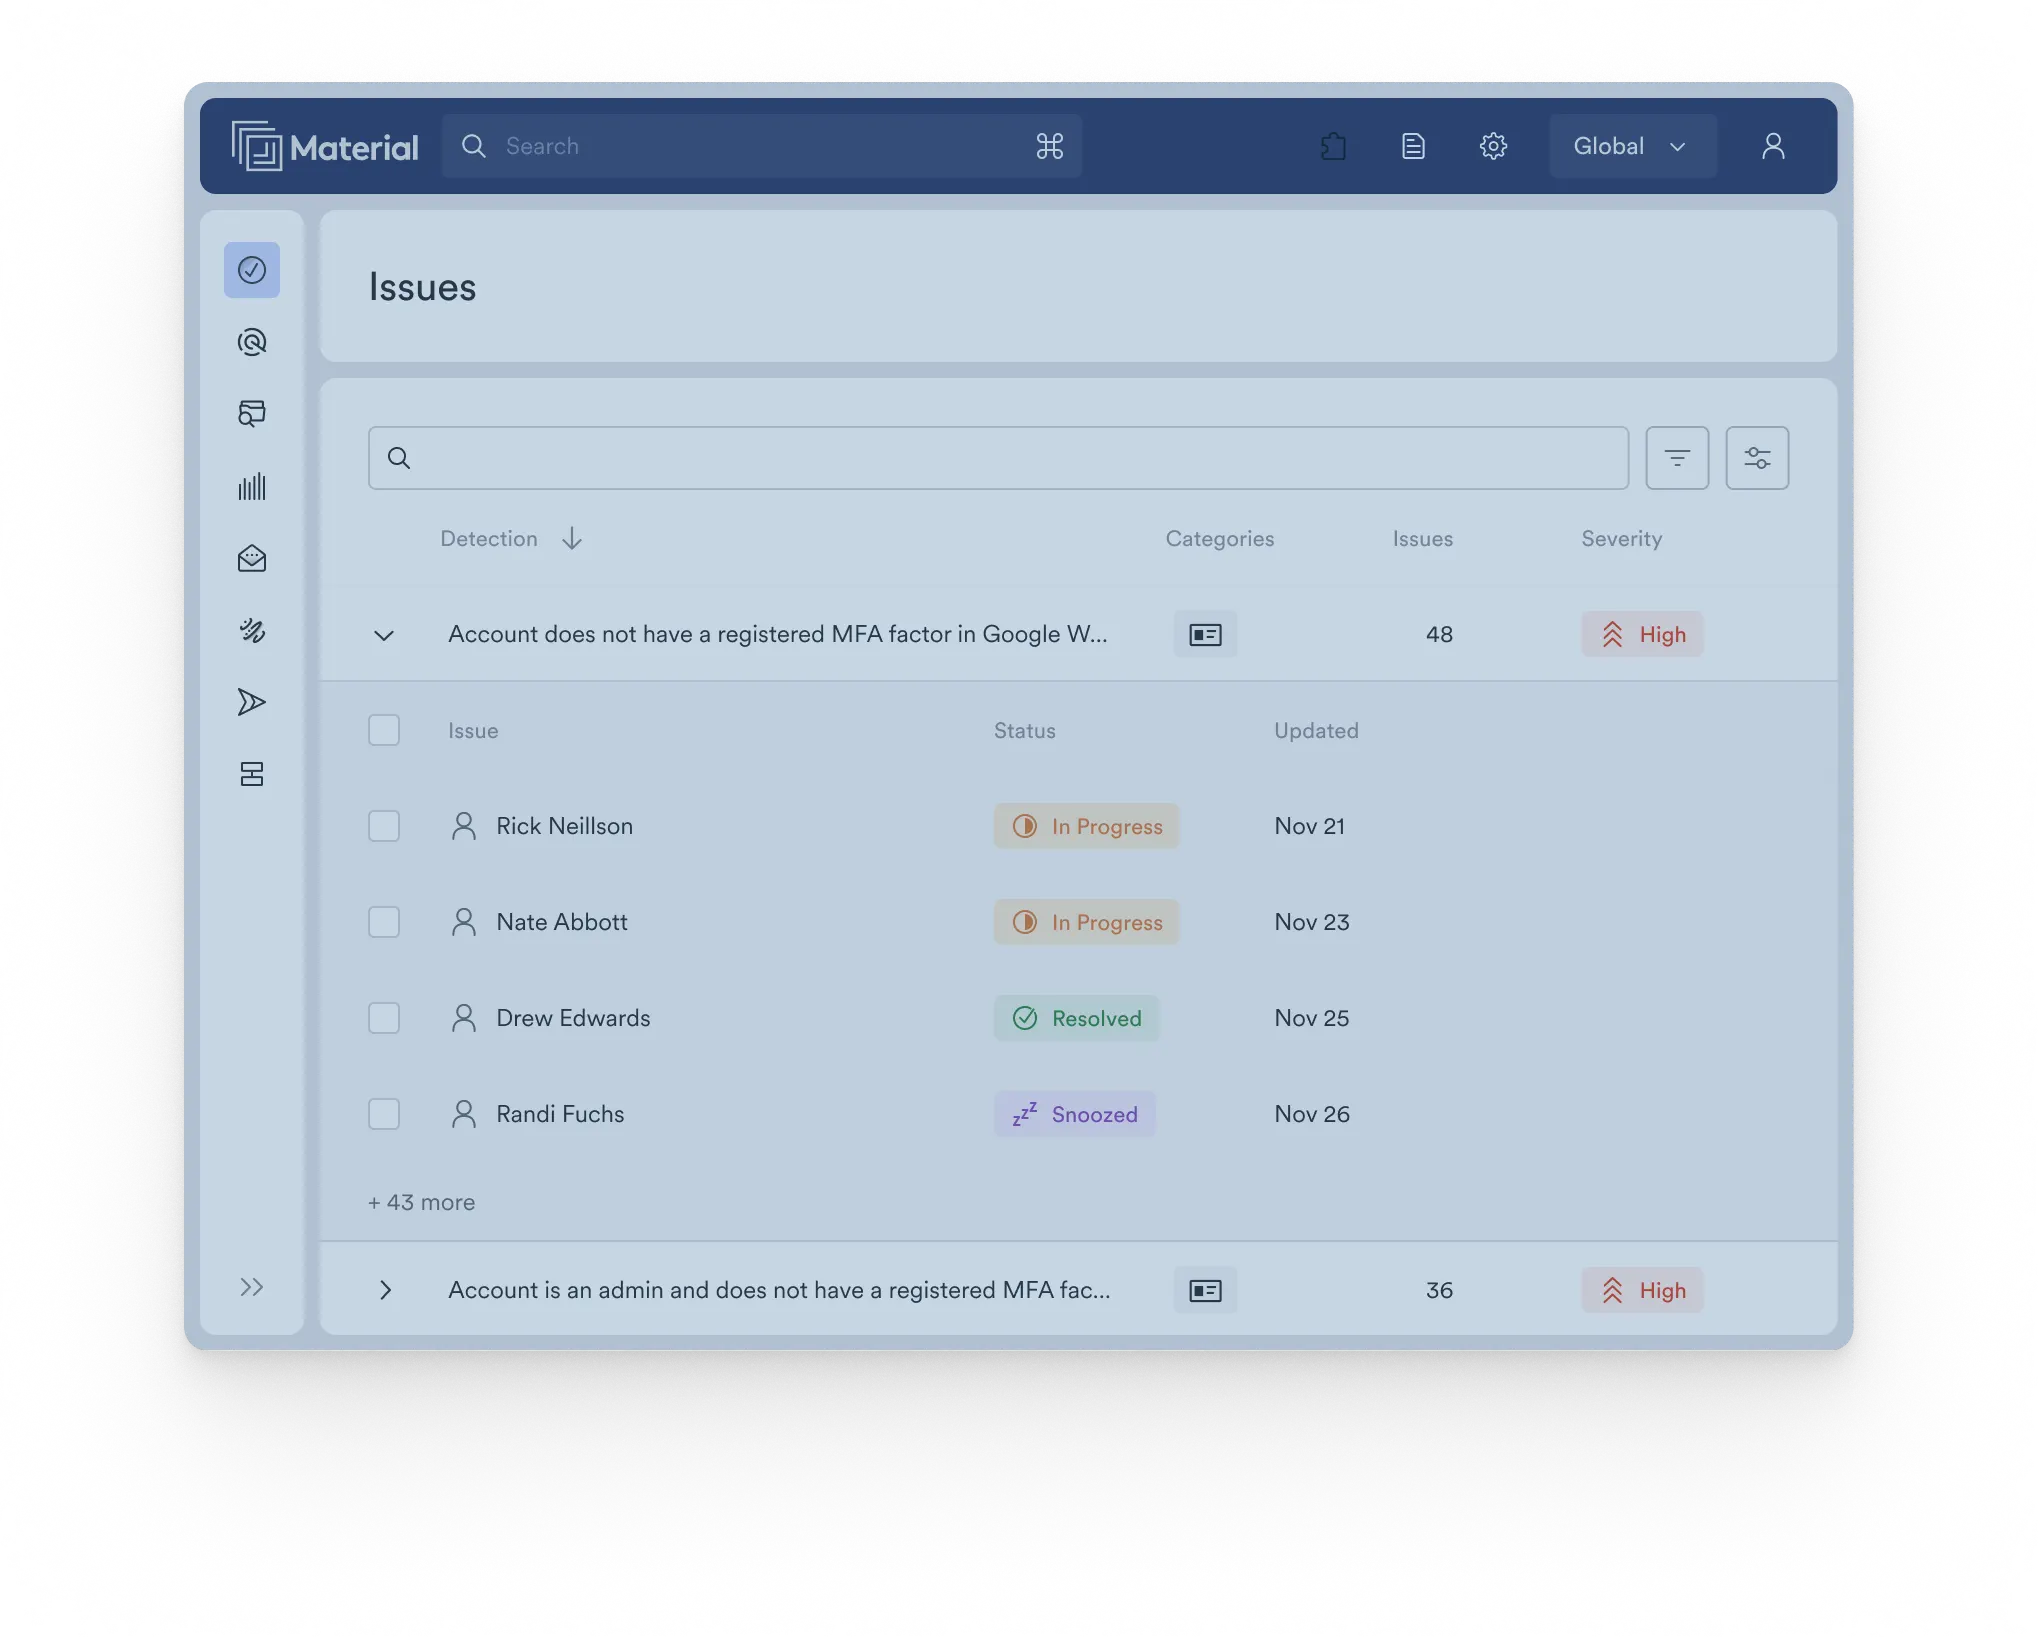
Material continuously monitors configuration state, identifies high-risk drift with context, and enables automated or one-click remediation to keep Google Workspace and Microsoft 365 aligned with your intended security posture.
Hear it from our customers
“”

The Challenge
Configuration drift quietly creates new security gaps
Your cloud workspace is not a static environment. It’s a complex, dynamic system with hundreds of settings spread across multiple admin consoles. Configuration drift—the slow, unintentional deviation from a secure baseline—is practically inevitable. It happens for many reasons: a help desk admin grants a "temporary" permission to resolve a ticket, a new feature is rolled out by Microsoft or Google with an insecure default, or different teams make changes without a central change management process.
- Growing security gaps A seemingly minor change, like enabling a new external sharing setting or altering a mail flow rule, can create a new, undiscovered vector for attackers. Over time, these small gaps accumulate into major vulnerabilities.
- Lack of central oversight With settings scattered across various admin centers (e.g., Entra ID, Purview, Defender, Google Admin console), no single person or team has a complete picture, making it impossible to know if the environment is actually configured as intended.
- Alert fatigue and noise Native auditing tools are often too noisy. They log every change, but lack the context to distinguish between a routine administrative action and a high-risk modification, leading to important alerts being missed.
- Compliance breaches An unmonitored change to data governance, sharing, or retention policies can silently pull your organization out of compliance with frameworks like SOC 2, HIPAA, or GDPR, which can be discovered too late during an audit.
Our Solution
Continuously detect and remediate risky changes
Material provides a clear, continuously monitored source of truth for your cloud workspace configuration, effectively preventing the slow decay of your security posture. Instead of reacting to incidents caused by misconfigurations, you can proactively maintain a desired state.
- Continuous monitoring and drift detection Material continually monitors your environment not only for events occurring across your cloud workspace, but for state changes as well. It automatically flags any change that deviates from your established security posture or is outside your risk tolerance. You no longer have to hunt for what’s changed; you get notified with precision.
- Prioritized, context-aware insight Material provides the context you need to act. It shows you exactly what changed, why it’s a risk (e.g., "This new mail forwarding rule was created on a C-level executive's account").
- Automated and one-click remediations The platform delivers guided, often one-click, remediations to revert changes to key configurations, as well as offering automated workflows that can instantly remediate upon given detections. This cuts through the noise and allows teams to focus on what matters.
Get a demo
Book a demo