The Challenge
Enterprise AI tools inherit existing permissions and can read, search, and act on anything in the inbox or Drive, which means every unresolved sharing mistake or unmanaged app instantly becomes new risk the moment AI is turned on.
Our Solution
Material discovers and classifies sensitive data, closes exposure gaps in Drive and email, and restricts what AI agents can read or act on, so organizations can adopt tools like Gemini, Copilot, and AI-native email assistants with confidence instead of catching up after the fact.
Hear it from our customers
“”

The Challenge
AI adoption moves faster than data governance
Security teams are under pressure to enable AI, not slow it down. But AI search tools plug into existing data with existing permissions, and AI agents can read, interpret, and act on anything already sitting in an inbox or Drive folder. Neither kind of tool comes with its own governance model. Whatever exposure already existed in the workspace becomes instantly and universally discoverable the moment AI goes live.
- AI Inherits Every Existing Permission Mistake A file that was technically accessible but practically hard to find becomes instantly discoverable the moment an AI search tool indexes it, turning years of quiet permission creep into an active risk.
- Agents Can Act on Anything in the Inbox AI email assistants read, search, and take action on messages the same way a human would, including pulling sensitive data into drafts or forwarding password resets and magic links without knowing they shouldn't.
- Shadow AI Arrives Before Sanctioned AI Does Employees connect AI tools to their work accounts long before security or IT has a rollout plan, so unmanaged AI risk is often already present before an official adoption even begins.
- No Security Team Wants to Be the Reason AI Is Blocked Slowing AI adoption to close every gap manually isn't a realistic option when the rest of the business is moving to adopt it regardless.
Our Solution
Catch up with AI access automatically
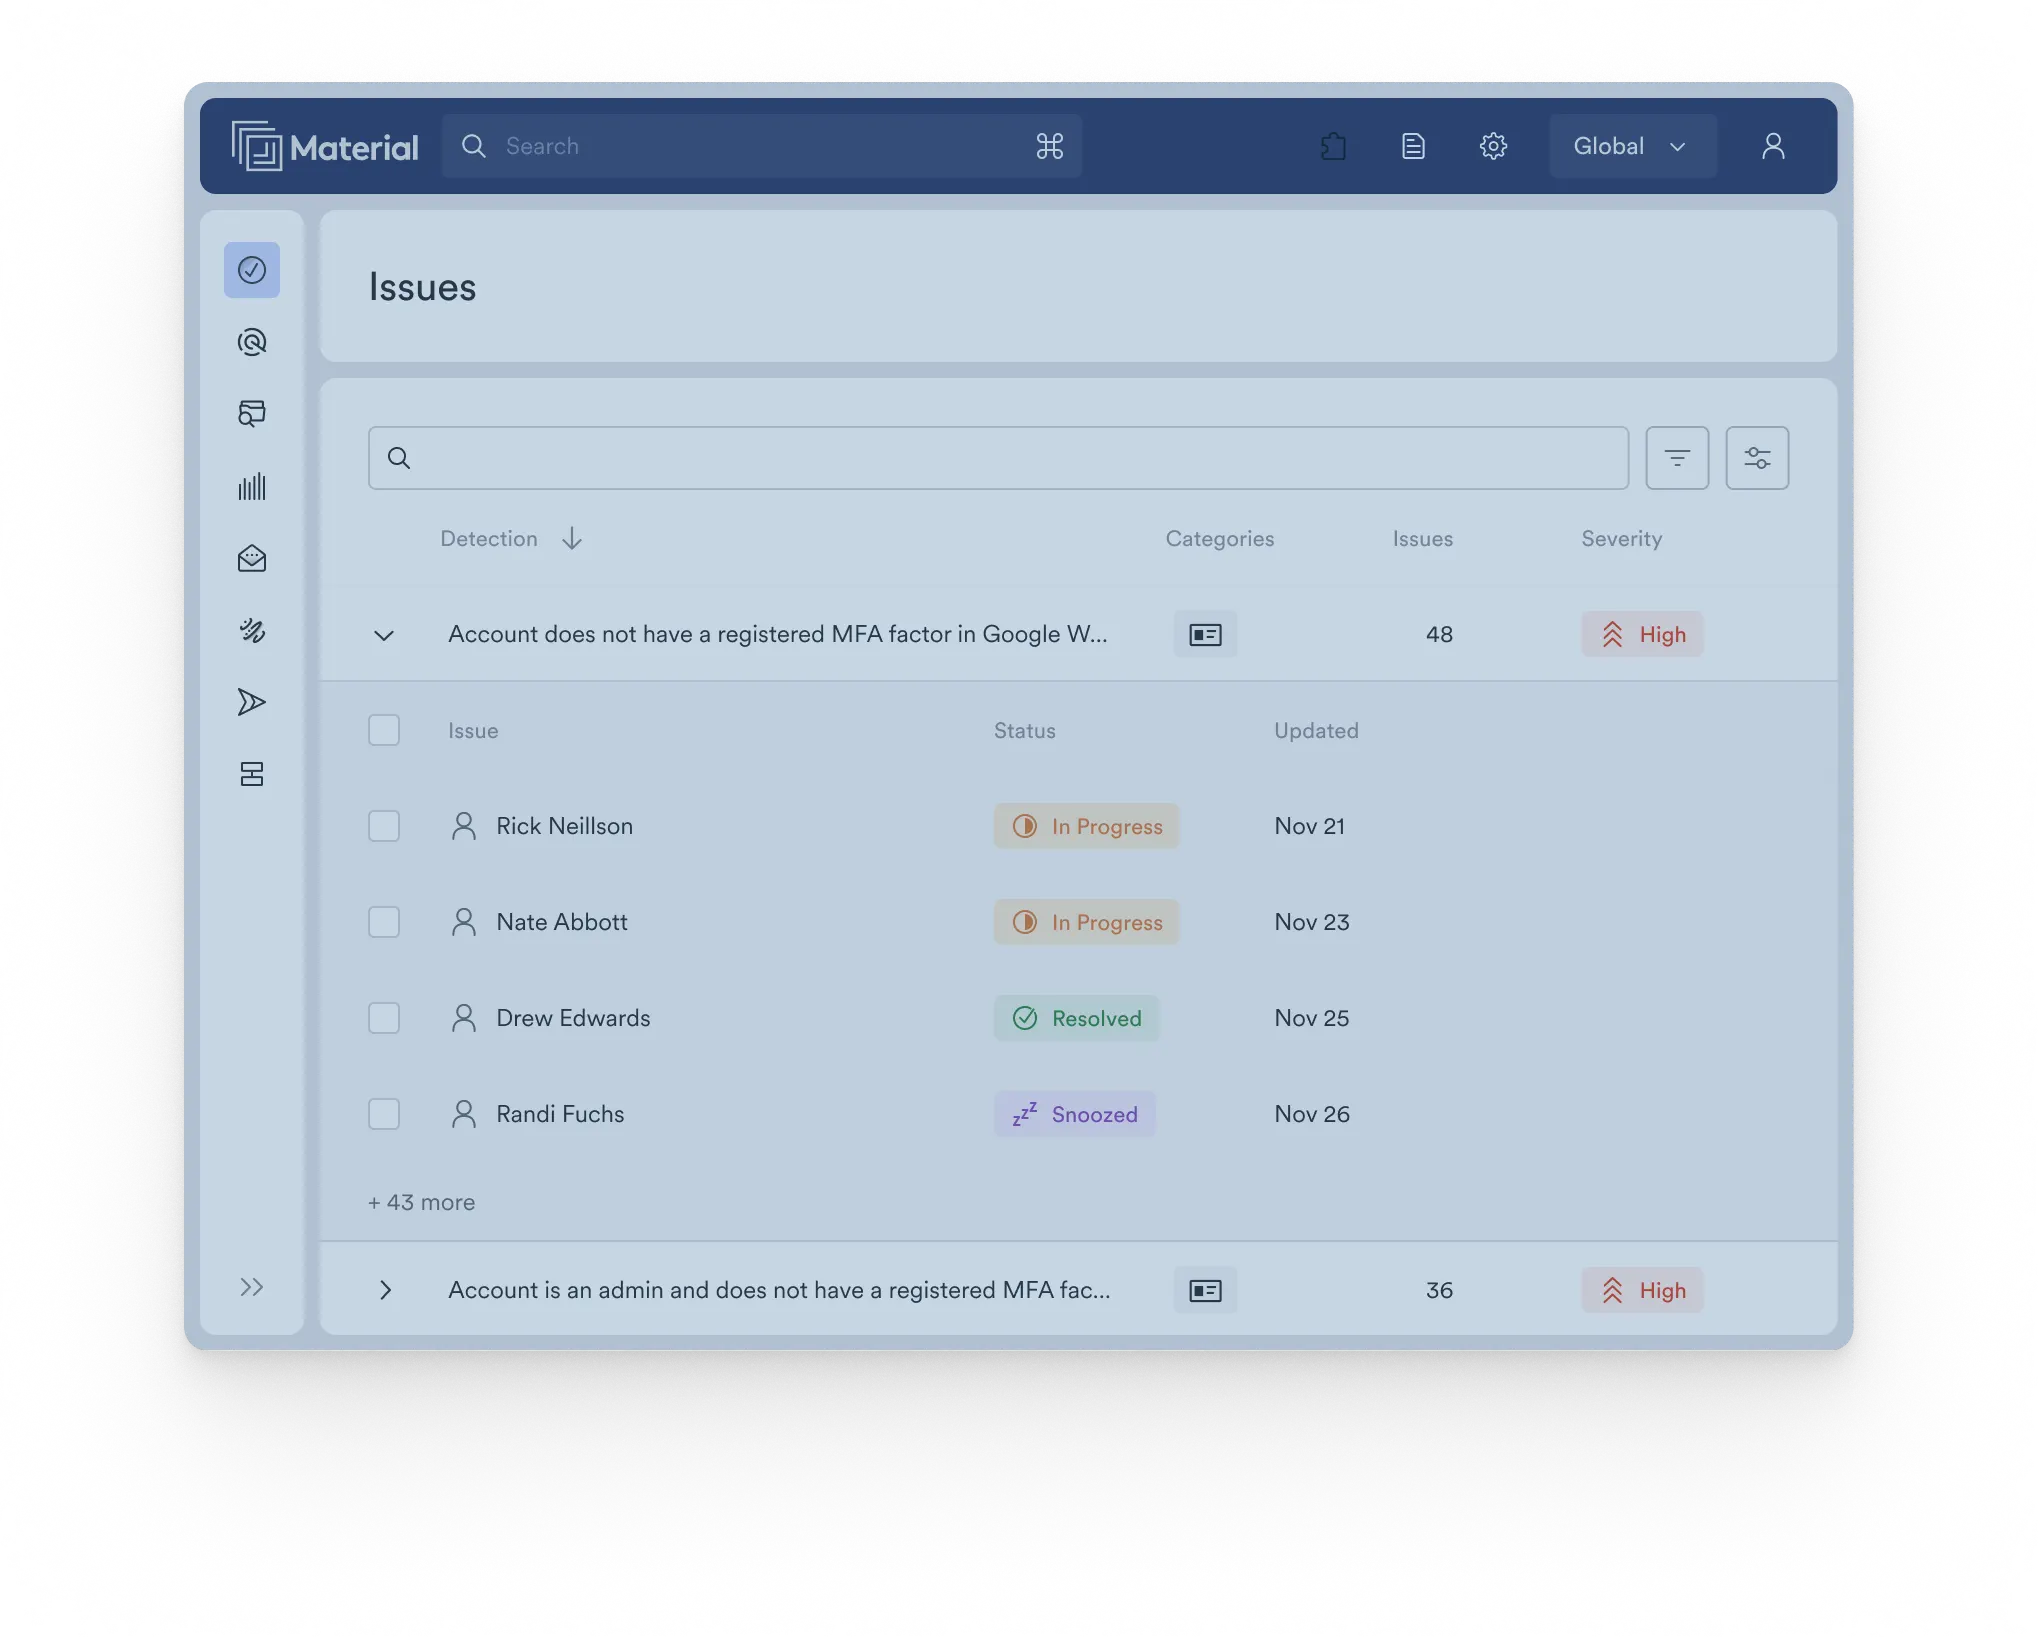
Material secures the data AI tools will touch, not just the AI tools themselves. Before a search rollout, Material finds and fixes risky permissions and toxic combinations of sensitive data so nothing gets surfaced that shouldn't be. For AI agents already operating in the inbox, Material identifies and protects sensitive content directly, so an agent can't act on what it can't read.
- Clean Up Exposure Before AI Search Goes Live Material discovers where sensitive data lives and automatically remediates risky permissions, public links, and personal-account sharing, so tools like Gemini and Copilot don't surface what shouldn't be found.
- Restrict What Agents Can Read and Act On Material identifies sensitive messages, password resets, and magic links, and requires a real-time MFA challenge before an AI agent, or a human, can access them.
- Discover Shadow AI Before It Becomes a Liability Material sees every AI tool and third-party app connected to the workspace, sanctioned or not, and assesses the real risk of each based on its access and behavior.
- Give Your Own Team's AI Agents Safe, Scoped Access For security teams building on AI themselves, Material's MCP server and API expose the platform's data through a standard interface, so an AI agent can investigate and act on threats without leaving its native workflow.