The Challenge
Years of sensitive email and files accumulate across the workspace with no consistent protection, so a compromised account, an overshared link, or a departing employee can each expose data that should never have been reachable in the first place.
Our Solution
Material continuously discovers sensitive content across email and Drive and applies protection directly to that data, so exposure from oversharing, offboarding, compromised accounts, or malicious apps gets contained at the source instead of relying on the access layer alone.
Hear it from our customers
“”

The Challenge
Sensitive data is exposed long before anyone notices
Most organizations can't answer a basic question: where does sensitive data actually live, and who, or what, can reach it right now? Sensitive content accumulates in email archives and Drive for years. Files get shared more broadly than intended. Employees leave without every sharing link they created getting revoked. Compromised accounts and malicious OAuth apps can each exfiltrate whatever data they land on with no additional resistance.
- Exposure Accumulates From Multiple Directions at Once Oversharing in Drive, unprotected historical email, offboarded employees' lingering access, and compromised accounts or apps all lead to the same outcome: sensitive data an attacker can reach without further effort.
- Native Tools Show Permissions, Not Risk Google Workspace and Microsoft 365 can tell you a file is shared externally, but not whether that file actually contains sensitive content, which is the detail that determines whether it matters.
- Point-in-Time Audits Are Already Out of Date By the time a quarterly Drive audit finishes, new files have been created and shared, and the picture it produced is already wrong.
- Once Data Is Reachable, There's Nothing Left to Stop It Traditional controls stop at the perimeter or the login. Once an account is authenticated or an app has a valid token, sensitive data behind that access has no further protection.
Our Solution
Protect the data itself, wherever it lives
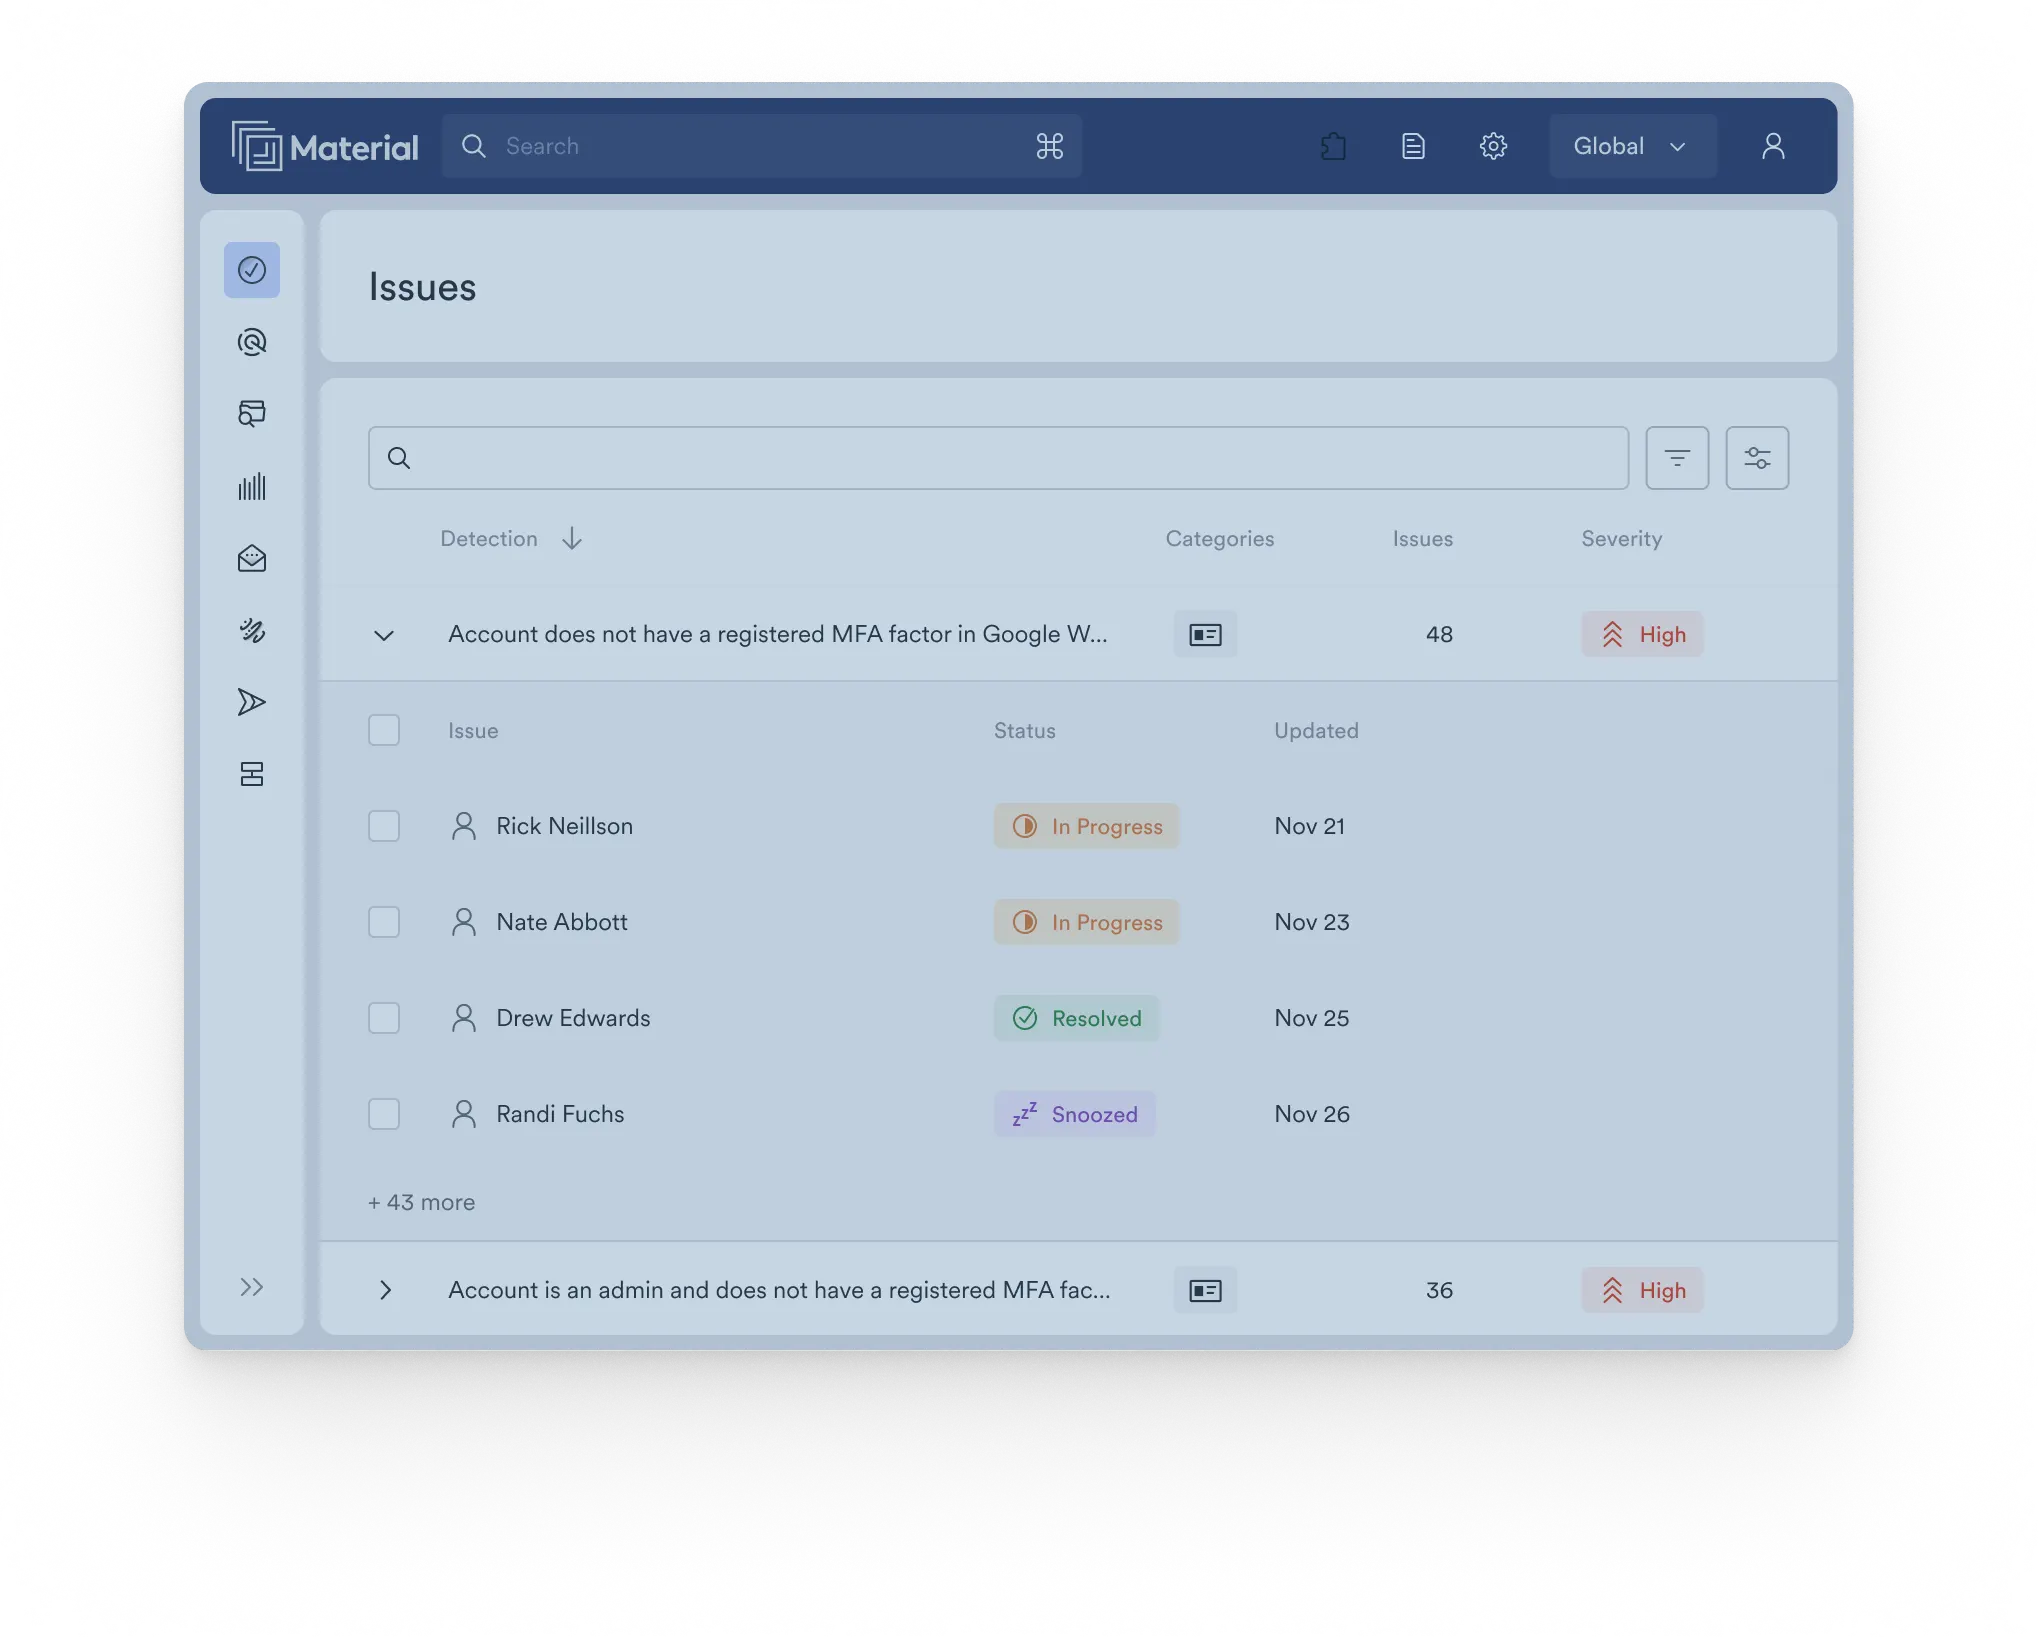
Material applies a zero-trust principle to sensitive data itself rather than just the accounts and apps around it. The platform continuously scans mailboxes and Drive to classify sensitive content, then applies proactive, policy-based protection, like requiring step-up authentication to view a sensitive message, so that even a successful account takeover, an overshared file, or a compromised app hits a wall at the data layer.
- Find Sensitive Data Wherever It's Hiding Material classifies sensitive content across every mailbox and Drive file, from day one to today, giving security teams a clear, actionable picture of what's actually at risk instead of a guess.
- Protect It With Policy, Not Reaction Material can require a real-time MFA challenge to access sensitive messages and files, configurable by data type, message age, and team, so protection is standing policy rather than something triggered only after a threat is detected.
- Contain Exposure at Every Point in the Lifecycle Material automatically finds and revokes lingering external sharing on files owned by offboarded employees, flags toxic combinations like sensitive files shared to personal accounts, and closes the gap between an audit and the next one.
- Stop Exfiltration Even After Access Is Granted Whether the access came from a compromised login or a malicious OAuth app, Material's protection sits at the data itself, so reaching an account or a token doesn't guarantee reaching what's inside it.