The Challenge
Point-in-time audits quickly become outdated as files, sensitive data, and sharing permissions constantly change, leaving security teams with blind spots and growing manual remediation work.
Our Solution
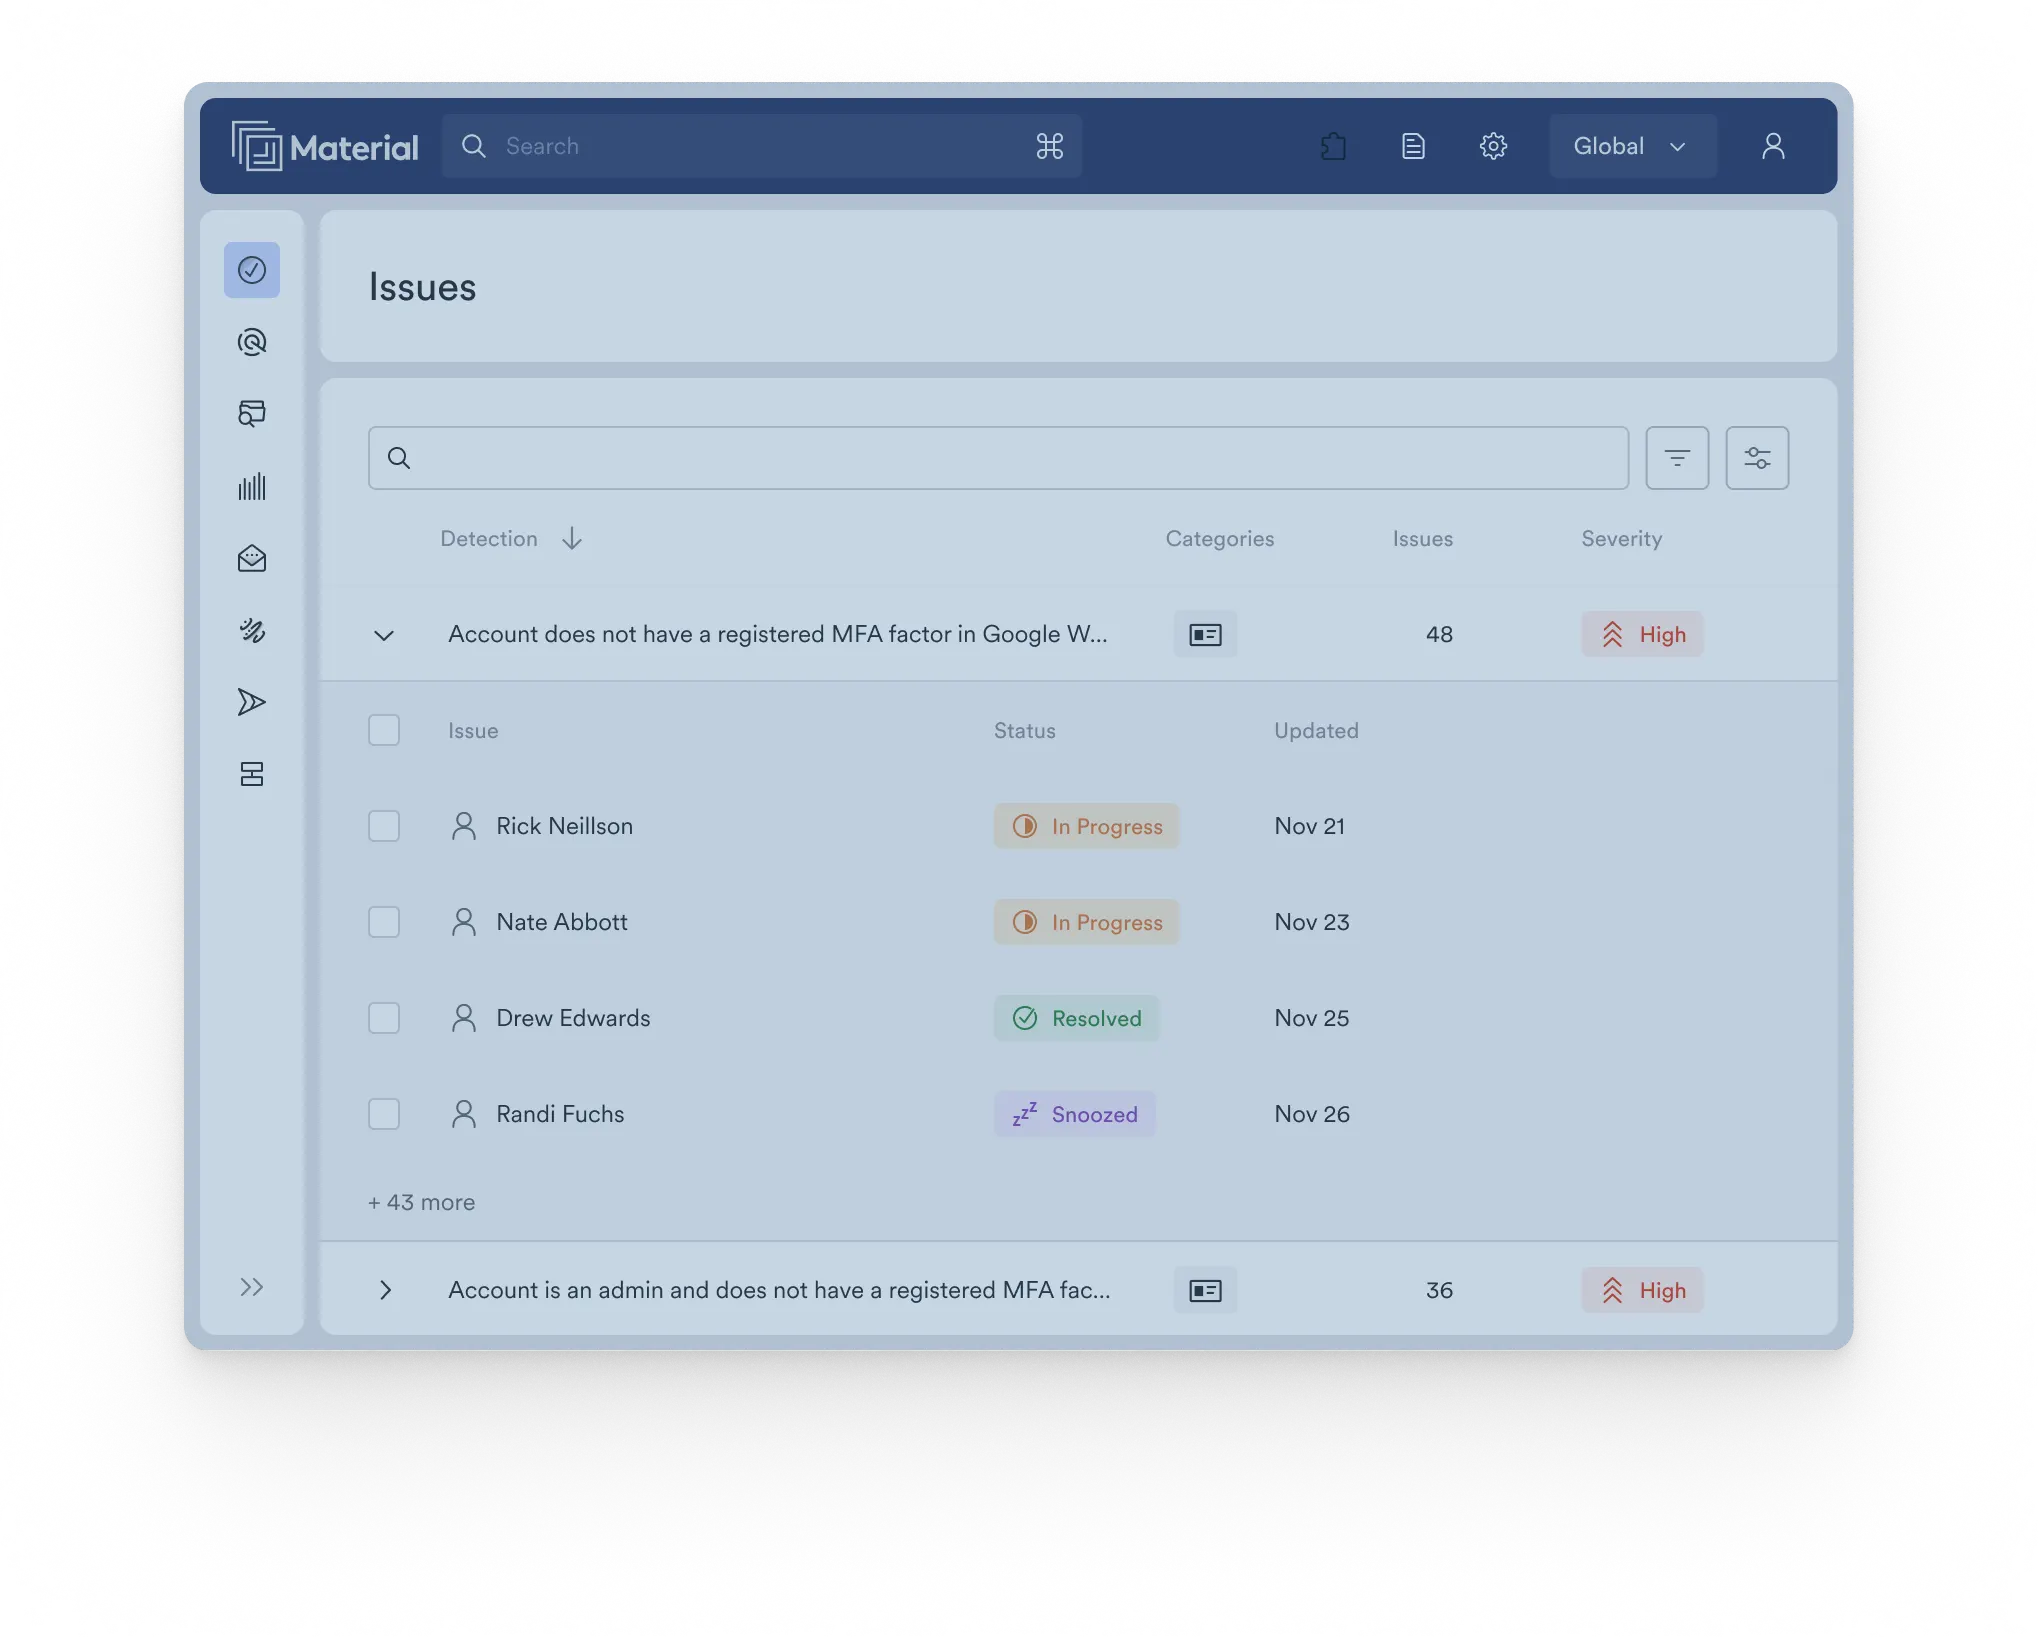
Material continuously monitors Google Drive content and permissions to surface high-risk sharing behavior as it happens and automate or streamline remediation before sensitive data is exposed.
Hear it from our customers
“We were relying on two things: Google Workspace's native security functionality and tooling and using an ad hoc Google Workspace auditor, but we knew this wouldn't scale as our company got bigger, which is why we came to Material.”
 Frank Wang
Lead Security Engineer, Headway
The Challenge
Periodic audits can't keep up
Relying on quarterly or even monthly audits of Google Drive is like trying to guard a bank by checking the security cameras once a week. The environment changes by the minute, and a static snapshot of permissions and data is immediately out of date. This leaves security teams struggling with significant blind spots in an era where threat actors are looking to exploit these gaps more aggressively.
- Data is dynamic Every day, employees create, upload, and share thousands of files. A clean report from last week provides zero assurance that a sensitive document wasn't just made public by accident five minutes ago.
- "Toxic combinations" are hidden The greatest risk isn’t just sensitive data or a public link in isolation; it’s the combination of the two. Google Workspace’s native security and traditional DLP tools lack the context to connect these dots, forcing teams to manually cross-reference data to find the real threats.
- Manual toil and burnout Running scripts or manually spot-checking files is an inefficient use of your security team's time. It doesn't scale with your organization's data growth and leads to inevitable human error.
- Compliance fire drills When an audit for SOC 2, HIPAA, or GDPR is on the horizon, teams are forced into a stressful, last-minute scramble to find and remediate issues, rather than simply proving an already-secure posture.
Our Solution
Continuous visibility and automated response
Material replaces the ineffective cycle of periodic audits with a real-time, continuous security program for your data in Google Drive. By monitoring content and permissions 24/7, Material allows you to find and fix risks as they happen.
- Always-on monitoring Material continuously scans Google Drive for new files, changes to existing content, and modifications to sharing permissions. You get a live, up-to-the-minute view of your data risk, not an outdated snapshot.
- Context-aware risk detection The platform automatically classifies data and analyzes sharing settings in tandem. It surfaces the truly critical risks by identifying toxic combinations: a spreadsheet containing PII shared with a personal gmail.com address, or a folder of legal documents accessible to anyone with the link.
- Automated and guided remediation Drastically reduce your team's workload. Material can be configured with automated policies to revoke public links on newly discovered sensitive documents. For other issues, it provides one-click workflows that allow an analyst to notify the file owner or revoke access directly from the Material console.
- An audit-ready posture Turn compliance from a periodic fire drill into a state of continuous readiness. With Material, you can confidently demonstrate to auditors that you have an active program for discovering and mitigating data exposure risks in your cloud workspace.