The Challenge
Aggressive email deletion policies sacrifice valuable business context and productivity without addressing the underlying risk: sensitive data remains exposed whenever an account is compromised.
Our Solution
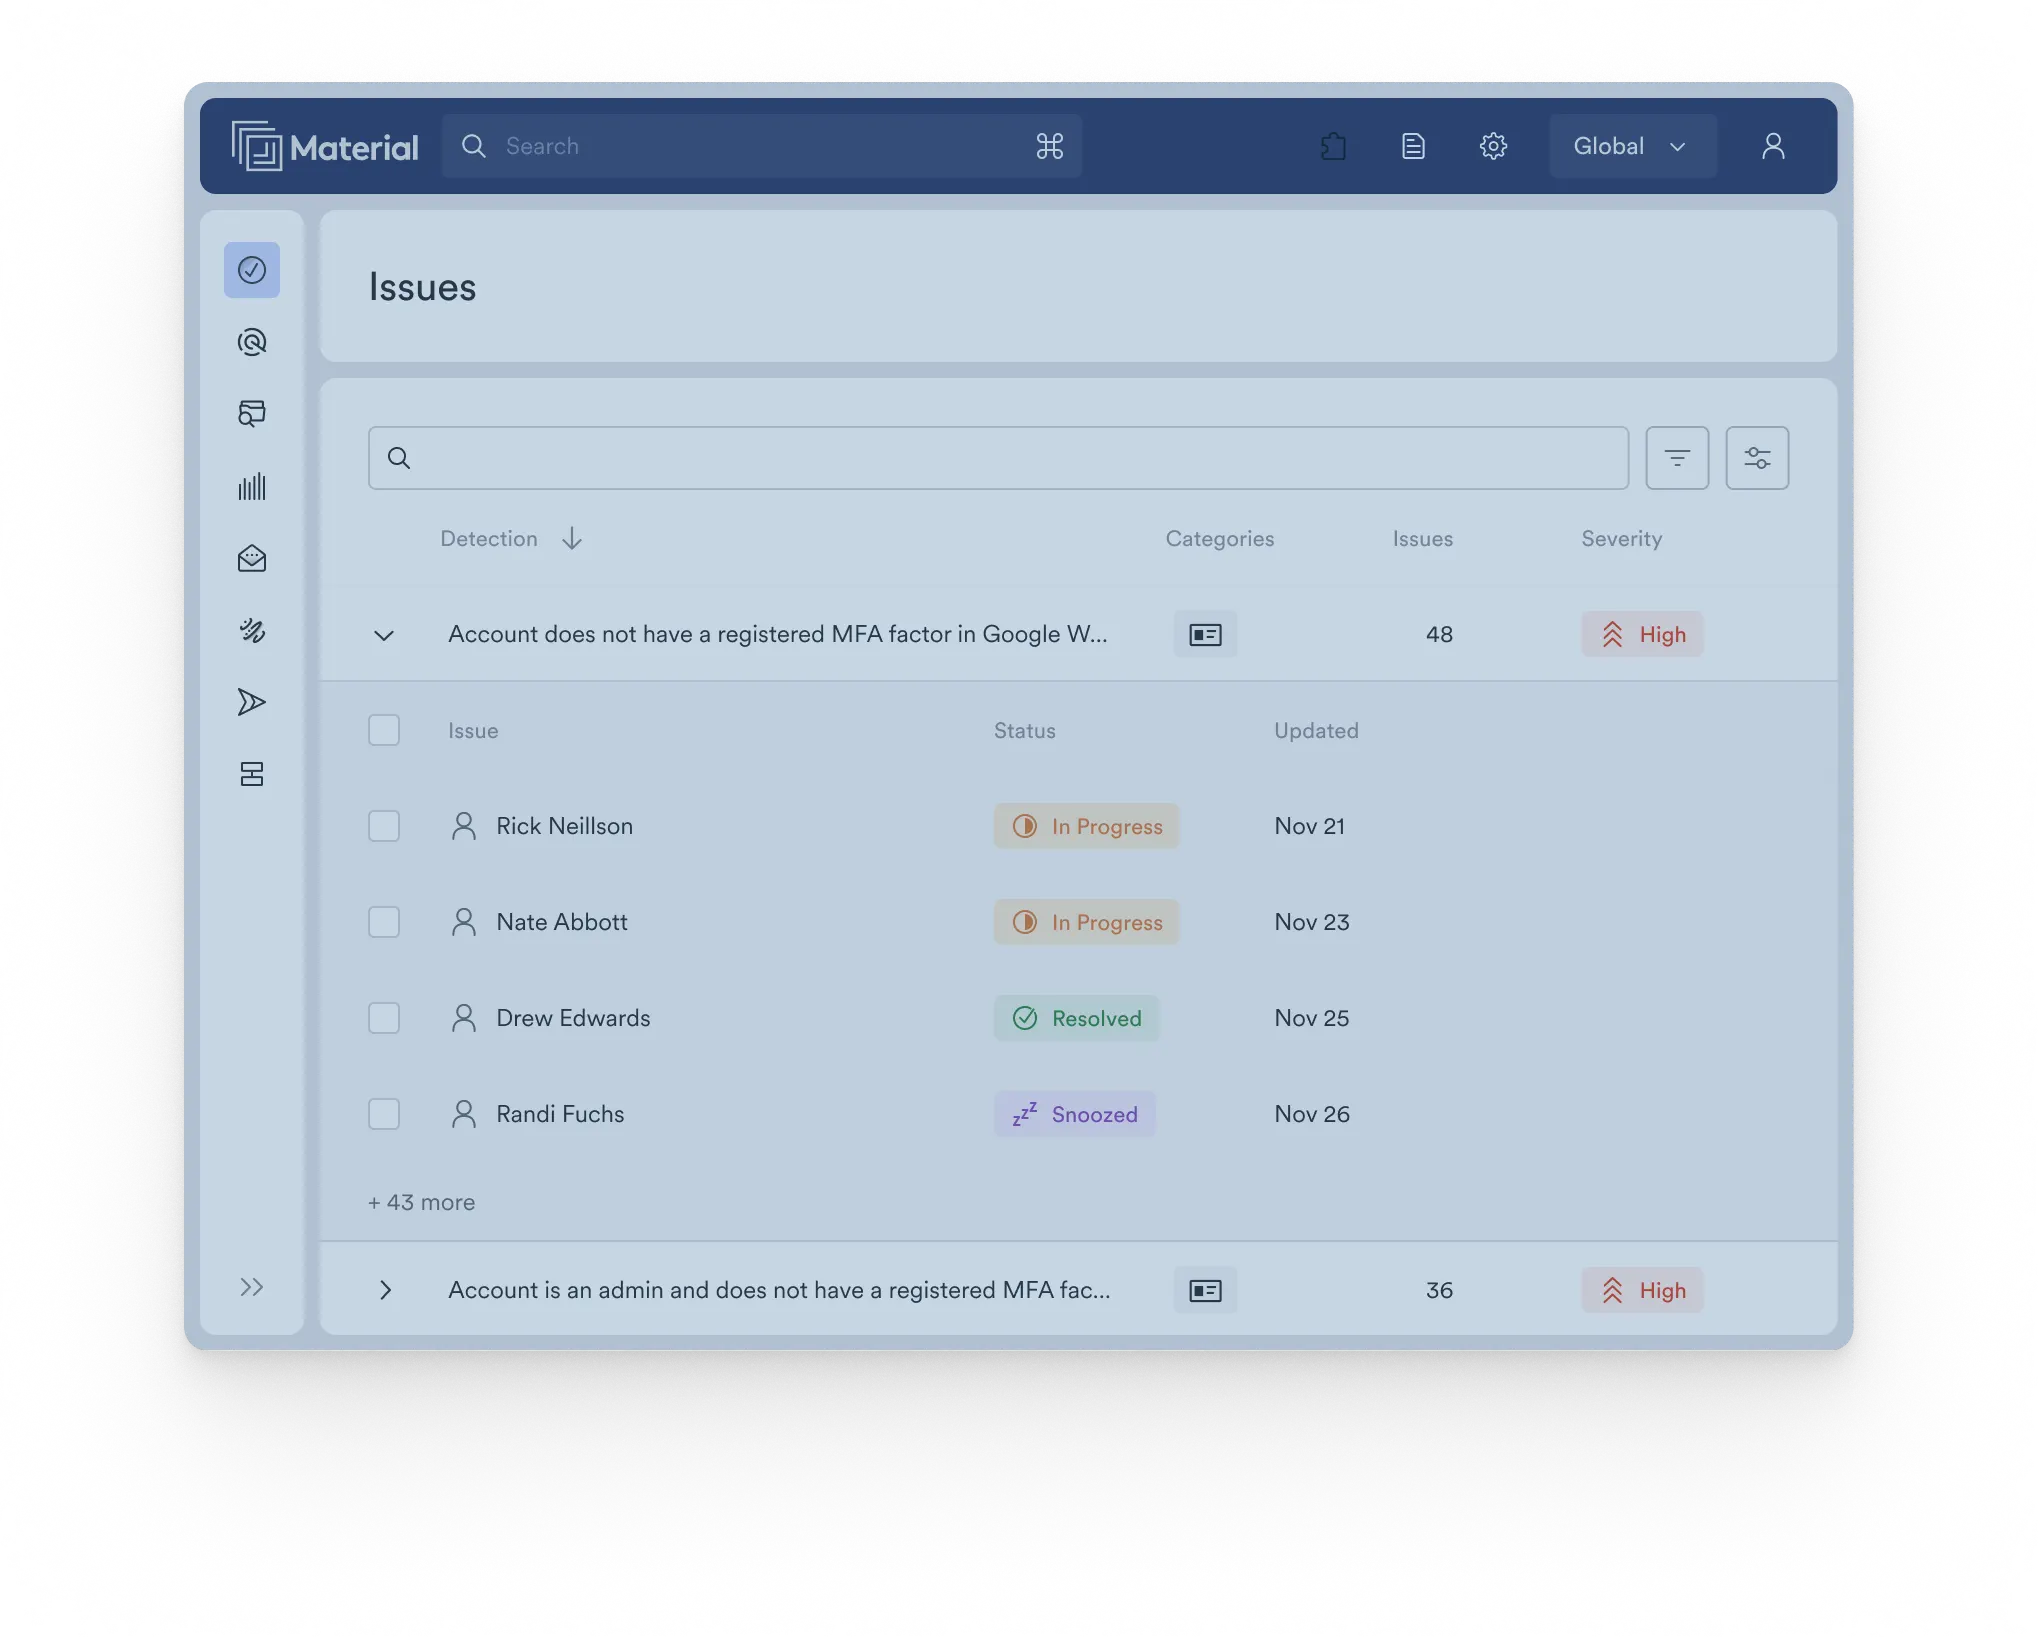
Material protects sensitive email at the message level with real-time MFA, allowing organizations to retain valuable data longer while keeping it inaccessible to unauthorized users.
Hear it from our customers
“Material’s solution is brilliant and simple. It enables you to protect the long tail of email while still keeping it available to employees. It helps protect us from day zero to whenever.”
 Veejay Leswal
VP, Technology & Cloud Operations, Oportun
The Challenge
Deleting data is a blunt and costly instrument
The default strategy for securing data-at-rest in email has been to get rid of it after a certain period of time. While well-intentioned, these aggressive deletion policies are a crude tool that creates significant friction for the business and fails to address the core risk.
- Business disruption When you delete emails after 90 days, you also delete years of valuable business context, contracts, and institutional knowledge. This forces employees to hoard information in less secure, unsanctioned locations just to do their jobs.
- The account takeover threat A user's mailbox is a treasure trove for attackers. A single compromised password can give a threat actor immediate access to every sensitive file and conversation that hasn't been deleted. Standard MFA at login does nothing to protect the data after the account is breached.
- Productivity drain Employees waste countless hours searching for information that has been purged or trying to work around policies. The burden of manually saving critical emails outside the mail client is a constant drag on efficiency.
- A compliance straitjacket To meet regulations like GDPR, CCPA, or HIPAA, many organizations feel their only option is the most extreme one—deletion—because they lack a more nuanced tool to protect data where it lives.
Our Solution
A Zero Trust approach to data in the mailbox
Material makes it possible to secure sensitive data without having to delete it. By applying a Zero Trust principle directly to the message level, you can allow employees to retain their data while ensuring it remains protected from even a successful account takeover.
- Protect sensitive messages with MFA Material can automatically find historical messages containing sensitive content (like financial data, PII, or legal documents) and redact their contents. To view the original message, the legitimate user must complete a real-time MFA challenge. Even if an attacker steals a user's password, the most valuable data remains locked and inaccessible.
- Enable secure, long-term retention By neutralizing the risk of data exposure from compromised accounts, Material allows you to confidently extend your retention policies. Business-critical information can remain in a useful, searchable location for employees, secured by a layer of protection at the message level.
- A familiar experience for users Accessing a protected message is simple. For the authorized user, it’s a quick, familiar MFA check within their mail client. This is worlds away from filing a ticket with IT and waiting for days to retrieve a message from a clunky archive.
- Granular, risk-based policies Move beyond one-size-fits-all deletion. Material allows you to create targeted policies based on risk. For example, you can automatically protect all emails older than 180 days that contain PII, or secure all messages from the executive leadership team, providing a more intelligent and flexible security model.